- +91 9867606024
- contact@controlera.in
- Home
- Risk Management Services
- Compliance
- Security
- Solution
- Training
- Contact Us
- Home
- Risk Management
Services -
Compliance
- Regulatory Audit
- Information System
Audit - IRDAI Audit
- SEBI Cyber Security & Cyber Resilience Framework Audit
- IRDAI Information & Cyber Security Assessment
- National critical Information Infrastructure Protection Centre (NCIIPC) Audit
- NABARD Security Audit For RRB
- Master Direction - Information Technology Framework for the NBFC
- Insurance Self Network Platform (ISNP) Audit
- Security
- Solution
- Training
- Contact Us
Our Team
- Home
- About Us

Professional Journey & Experience
- 30 years of BFSI industry experience in Nationalized Bank, Private Sector Bank, Multinational Bank and Startup Bank
- Professional qualifications : CISA, CISSP, CRISC, CeISB, CAIIB, ISO 9001:2008, ISO 27001:2005 Lead Auditor, ISO 22301 BCMS Lead Implementor
- Erstwhile member of IT Strategy Committee, IT Steering Committee, Information Security Council, Product Evaluation and Architecture Review Committee, Risk Management Committee, Enterprise and Operational Risk Management Committee
- Developed and implemented Technology Risk Management Framework, IS Audit Manual, IS Audit Policy, IT and IS Standard Operating Procedures (SOPs), IT Risk Policies, IT Risk Standards and Risk Registers
- Information Technology and Information Security audit and setup experience in Information Security Architecture and various domains like Core Banking, Credit Card, ATM, Mobile Banking, Email Management System, Data Centre-Business Continuity Centre, Security Operations Centers (SOC),VA/PT, Infrastructure Audit, Third Party Risk Management (Vendors)
- Conducted Information Systems & Security Architecture audit of Overseas Branches (Hong Kong, Shanghai & Colombo)

Mr. Rupesh Kumar Srivastava
Founder & CEO
- Expertise includes Application audit, Vulnerability Assessment of OS and DB, Effectiveness of BCP & DRP and IT Service Management.
- Worked on all domains of Information security viz. Enterprise, Infrastructure, Application, Data Protection and Privacy
- Strong working knowledge of Financial, Operational, Compliance and Systems Auditing Techniques
-
Specialties: Developing Information Security Strategy
- Risk management process
- Expertise in review of Information Technology and Information Security Processes & Risk Control Matrix
- Incident Management process
- Information Security metrics
- Developing data protection and data privacy strategies

Professional Journey & Experience
- Bachelor of Arts from Lucknow University
- Ensures smooth coordination between teams.
- Maintains internal processes, policies and daily operations.
- Encourages a transparent and supportive work culture.
- Known for being dependable, detail-oriented and solution-focused.
- Supports strategic planning through consistent internal alignment.
- Fosters unity, clarity and accountability across the team.

Mrs. Nidhi Srivastava
Co-Founder & Head Internal Affairs

Professional Journey & Experience
- Qualifications includes B.Sc. (Physics Honors), CISA, CISM, CRISC from ISACA & ISO 27001 Lead Auditor and implementor
- Has more than 45 years of experience on the Banking and Cyber Security and information Technology and Security Sector
- Has server State Bank of India for 30+ Years
- Has been Information Systems Audit head in Axis Bank between April 2005 and September 2010
- Has been Chief Information Security Officer in Axis Bank between September 2010 and September 2013
- Has featured among the Top-100 CISO across the country repeatedly from 2013 till 2019 from CISO Platform, Bangalore

Mr. Nabankur Sen
Advisor

Professional Journey & Experience
- Qualification includes CISSP, CISA, CRISC, CIA, GDPR for Security Professionals Certificate, ISO 27001 LA, ITIL (Found.)
- Has more than 40 years of experience in the Banking, Information Systems Security and Information Systems Audit.
- Chief Manager, Information Security Department, State Bank of India
- Asst Vice President, Information Systems Audit, Axis Bank
- Manager, IT Audit, Al Rajhi Bank
- Chief Internal Auditor of an overseas bank
- Conducted corporate training programs for CISSP and CISA for leading multinational organizations
Worked at senior levels in banks in India and overseas:

Mr. Daniel Sunil Mahanty
Advisor
Professional Journey & Experience
- Over 45 years of experience in IT and Information Security
- Worked for IIM Lucknow in the IT Department
- One of the founder members of Information Security Department of SBI
- Ex Member of Information Security Committee formed by IDRBT for Banks
- Post Graduate in Economics and Statistics
- Certified from IIT Kanpur in Programming and DBMS
- Certifications: CISA, CISB, ISO:27001 LA, BS:25999 LA, CCNA
- Certified Independent Director
- Domain expertise in drafting IT and IS Policies and Procedures, Outsourcing Policies and Procedures
Professional Qualifications
Domain Expertise
Mr. Naveen Shrivastva
Advisor
Professional Journey & Experience
- 25+ years of comprehensive expertise in IT auditing, risk management, and regulatory compliance in the banking and financial services sector.
- Certified Information Systems Auditor (CISA), USA, 2016
- CAIIB – Indian Institute of Banking and Finance, October 2010
- M.Phil. (Computer Science)
- MCA (Master of Computer Applications)
- B.Sc. (Computer Science)
- Expertise in internal controls assessment, technology risk evaluation, and banking IT systems, including core banking solutions, automation initiatives, and compliance audits.
- Well versed with Regulatory Compliance Audit and Mitigation.
- Proficient in SQL, Microsoft Office, and data analysis tools to support audit accuracy and reporting.
Professional Qualification
Educational Qualification
Areas of Expertise
Mr. P. Singaravelu
Whole Time Director

Professional Journey & Experience
- 25 years’ experience in designing, implementing and auditing enterprise-wide Business Continuity Management Frameworks, aligned to industry Standards.
- Professional qualifications : ISO 22301: 2019, BCMS- Lead Auditor, 2022, Certified IT Disaster Risk Engineer, 2021.
- Certified Risk Professional: ISO 22301:2012, Certified Business Continuity Professional (CBCP): Disaster Recovery Institute International, New York, 2006
- Certified Information Systems Security Officer, 2023.
- Certified Information Systems Auditor (CISA)
- Certified Accredited Professional from Fire and Security Association of India, 2023.
- Certificate Course in Disaster Management: MSME Technology Center, GOI, Oct 2018.
- Post Graduate Degree in Fire Protection and Safety: MIT, Pune, 2017
- MBA (Fire Protection and Safety Management): Jaipur National University, 2017
- Worked with global enterprises, exposure to world-class practices in Governance, Risk and Compliance in Business Continuity Management, IT Disaster Recovery, Enterprise Risk Management, Third Party Risk Management, Cyber Resilience, Operations Risk Management, Health and Safety
- Held Management level positions as General Manager, IBM – in Global Business Continuity Management role;
- Provided strategic direction for BCM, IT DR and Third-Party Risk Management Programs for Deutsche Bank, Barclays Bank and for Clients of KPMG, EY and IBM.
- Has conducted over 100 Crisis Simulation Exercises, over 500 Live IT Disaster Recovery Drills, over 800 BCM Drills across 3 Countries.

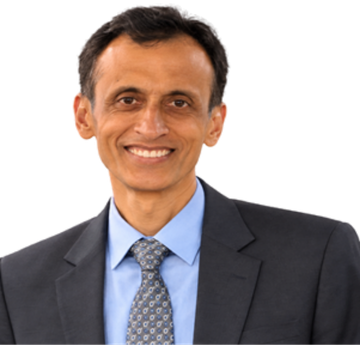
Mr. Rohit Verma
Head – Risk Advisory & Enterprise Resilience
Professional Journey & Experience
- 30+ years of experience with State Bank of India, Axis Bank, and IndusInd Bank in Banking Operations, Credit Risk, IT/IS Audit, Third Party Risk Management, Regulatory Compliance, and Gap Assessment.
- B.Sc. (Physics, Chemistry & Mathematics), Bangalore University
- CISA (Certified Information Systems Auditor), ISACA, USA
- CIA (Certified Internal Auditor), Institute of Internal Auditors, USA
- CRISC (Certified in Risk and Information System Control), ISACA, USA
- CAIIB (Certified Associate of Indian Institute of Bankers)
- Head – IS Audit, IndusInd Bank, 2012 – 2025
- Head – IT / IS Audit, Axis Bank, 2010 – 2012
- Chief Manager – State Bank of India, Audit & Inspection, Credit Operations, Foreign Exchange, 1986 – 2009
- Internal Audit & IT/IS Audit, IT Infrastructure & Applications Assessment, and Data Centre Assessment
- IT and IS Policy, Process, Framework Documentation
- Risk & Compliance Management
- Banking Operations including Retail, Credit, Trade Finance, and Remittances
- Credit & Operational Risk Management
- Third Party Risk Management
- Regulatory Guidelines Compliance Assessment
- Regulatory Compliance Gap Assessment and Mitigation
Education
Certifications
Professional Experience
Areas of Expertise
Mr. Rajanikant Pathak
Head - Risk Advisory & ISMS